Can Your Credit Union Spot a Deepfake? Five Cybersecurity Controls That Matter Most
October 22, 2026
By: David Bryant, Chief Information Security Officer, Velera
Cyber threats are constantly evolving. While artificial intelligence (AI) offers significant opportunities for innovation and efficiency, it is also enabling increasingly sophisticated fraud schemes that exploit human trust rather than technical vulnerabilities.
Guidance from America’s Credit Unions highlights concerns regarding the use of AI-generated content — including deepfakes — to facilitate fraud, impersonation and account takeover attempts.
Understanding Deepfakes and AI-Enabled Social Engineering
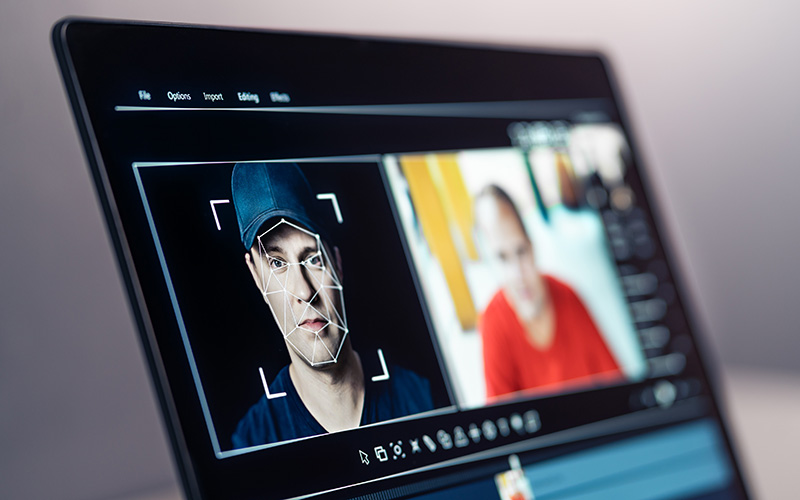
A deepfake is AI-generated or AI-manipulated content, such as voice recordings, videos, images or text, designed to resemble a real person or legitimate communication. As AI tools become more accessible, cybercriminals can create convincing impersonations of executives, employees, clients, vendors or trusted business partners.
Unlike many traditional cyberattacks, these deepfake social engineering schemes typically do not rely on exploiting software vulnerabilities. Instead, they rely on social engineering — exploiting urgency, trust and human decision-making to persuade individuals to take actions they otherwise would not.
Why Credit Unions Should Pay Attention
Financial institutions have long been targets of fraud due to their role in processing and safeguarding financial transactions. According to FinCEN, financial institutions have reported increasing suspicious activity involving the use of deepfake media, including fraudulent identity documents and attempts to circumvent identity verification and authentication controls.
Credit unions may face unique challenges. Lean staffing models, the need to process transactions efficiently and the high levels of trust that members have in their credit union can create opportunities for fraudsters seeking to exploit established business processes. Even experienced employees and savvy members can be deceived when a request appears to originate from a trusted source.
Common AI-Enabled Fraud Scenarios
Here are a few common AI-enabled fraud scenarios to be on the look out for:
- Executive Impersonation — Imagine one of your employees receiving a voicemail that sounds exactly like your CEO, directing the employee to approve an urgent wire transfer before the close of business. The voice may sound authentic, but the request could be fraudulent. Executive impersonation is one of the most significant risks associated with deepfake technology. One firm lost $25M in a deepfake scam where an employee thought he was talking to senior leadership at his company.
- Vendor Payment Fraud — Attackers may use AI-generated emails and voice communications to request changes to vendor banking instructions or payment processes. These communications can appear legitimate and may be difficult to distinguish from genuine business correspondence.
- Customer Identity Fraud — Criminals are increasingly leveraging AI-generated media to support identity fraud schemes. Synthetic or altered identity documents are being used to bypass customer authentication and verification controls.
- Employee Credential Theft — AI-generated phishing emails can be personalized, grammatically correct and tailored to specific organizations or individuals. As a result, employees may be more likely to engage with malicious messages or disclose credentials.
Five Cybersecurity Controls Credit Unions Can Implement Today
Technology alone won’t eliminate cybersecurity risks. Effective controls combine people, processes and technology. Does your credit union have these protocols in place?
- Verify requests through independent channels. Require your employees to independently verify requests involving wire transfers, payment instructions, sensitive information or changes to account details using a known and trusted communication channel. Never rely solely on information provided in a suspicious email, text message or voicemail.
- Strengthen approval processes. Establish dual authorization requirements for high-risk transactions and ensure appropriate segregation of duties. These controls can help prevent a single individual from authorizing a payment based solely on an impersonation attempt.
- Update security awareness training. Employees should understand that modern fraud extends beyond traditional phishing. Training programs should include examples of AI-generated communications, executive impersonation schemes and deepfake-enabled fraud scenarios to help educate employees. Educational resources and training should be regularly updated.
- Rehearse incident response procedures. Credit unions should ensure employees know how to report suspicious communications and escalate potential fraud attempts. Regular testing and tabletop exercises can improve preparedness and response effectiveness.
- Include AI threats in risk assessments. Risk assessments should be updated to address emerging AI-related threats and evaluate whether current controls remain effective. Threat landscapes continue to evolve — and your credit union’s risk management framework should evolve with them.
Questions for Leadership
Boards of Directors and senior management need to consider the following when examining cybersecurity protocols, which they should do regularly:
- Could a single employee authorize a high-risk financial transaction?
- How are executive, vendor and member requests independently verified?
- Have employees received training on AI-enabled fraud and deepfake threats?
- Are AI-related risks incorporated into the credit union’s risk assessment process?
- Would existing controls effectively identify and prevent an impersonation attempt?
Deepfakes and AI are changing the way cybercriminals conduct fraud and social engineering attacks. While the technology behind these schemes may be ever-evolving, the objective remains the same — exploiting trust to gain access to money, systems or sensitive information.
Credit unions that combine strong governance, vigilant employees and disciplined verification practices will be better positioned to protect themselves and maintain member trust despite the risks posed by deepfakes.
To learn more about Velera and the solutions they offer to help keep your credit union and members safe from cybersecurity threats, connect with the GoWest Solutions Team today.
Posted in Compliance Resources, GoWest Solutions.
Brittanie Bonanzino
AVP, Communications
Washington
Phone: 509.218.1192
Toll-free: 800.995.9064
Alyse Knudsen
Manager, Communications
Oregon
Phone: 971.450.5660
Toll-free: 800.995.9064
Madlynn Schreibvogel
VP, Public Relations
Colorado
Phone: 303.513.3765
Toll-free: 800.995.9064